OpenID Foundation: The Solution to Insecure Phone Identity Verification Already Exists
By Katrine Thielke on 22 October 2026
After the massive Danish CPR data breach, the international standards organization OpenID Foundation is urging companies and government agencies to adopt open standards for digital identity verification, including over the phone. The organization points to the CIBA standard, which lets you verify a caller's identity digitally without asking traditional security questions.
We don't need to develop new technologies to replace CPR numbers, dates of birth, and addresses as means of identity verification. We already have international standards that make it possible to integrate strong digital authentication into e.g. customer service.
The OpenID Foundation makes this clear in a new blog post about the leak of information on 8.8 million people from Denmark's Central Person Register (CPR); the Danish CPR number is a person's identification number, and many companies still ask callers to confirm it to prove who they are.
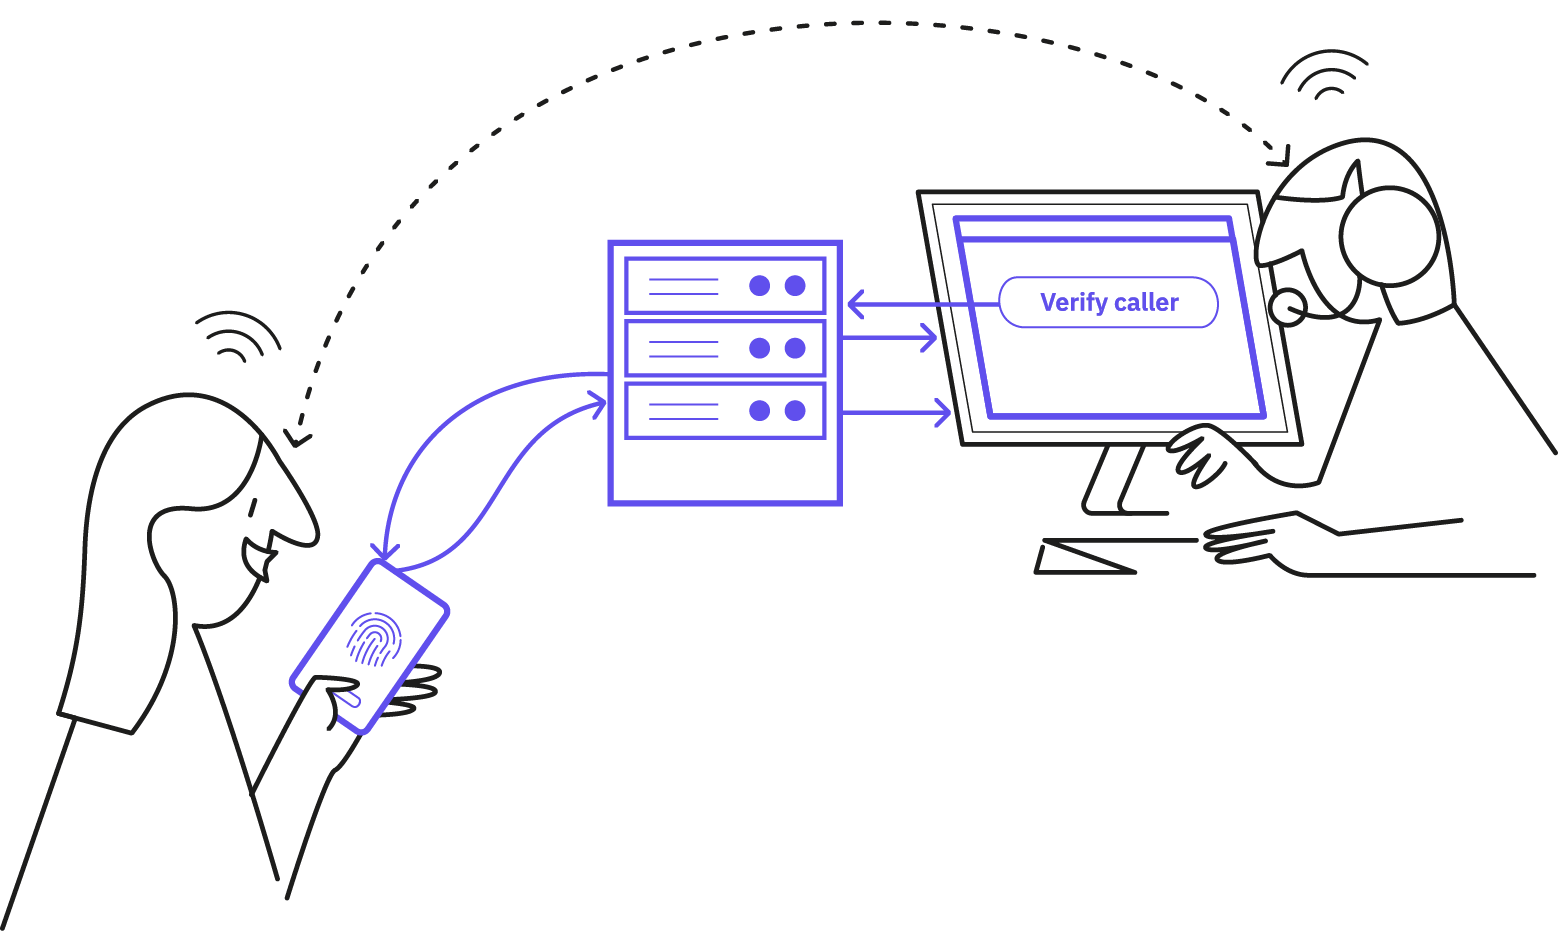
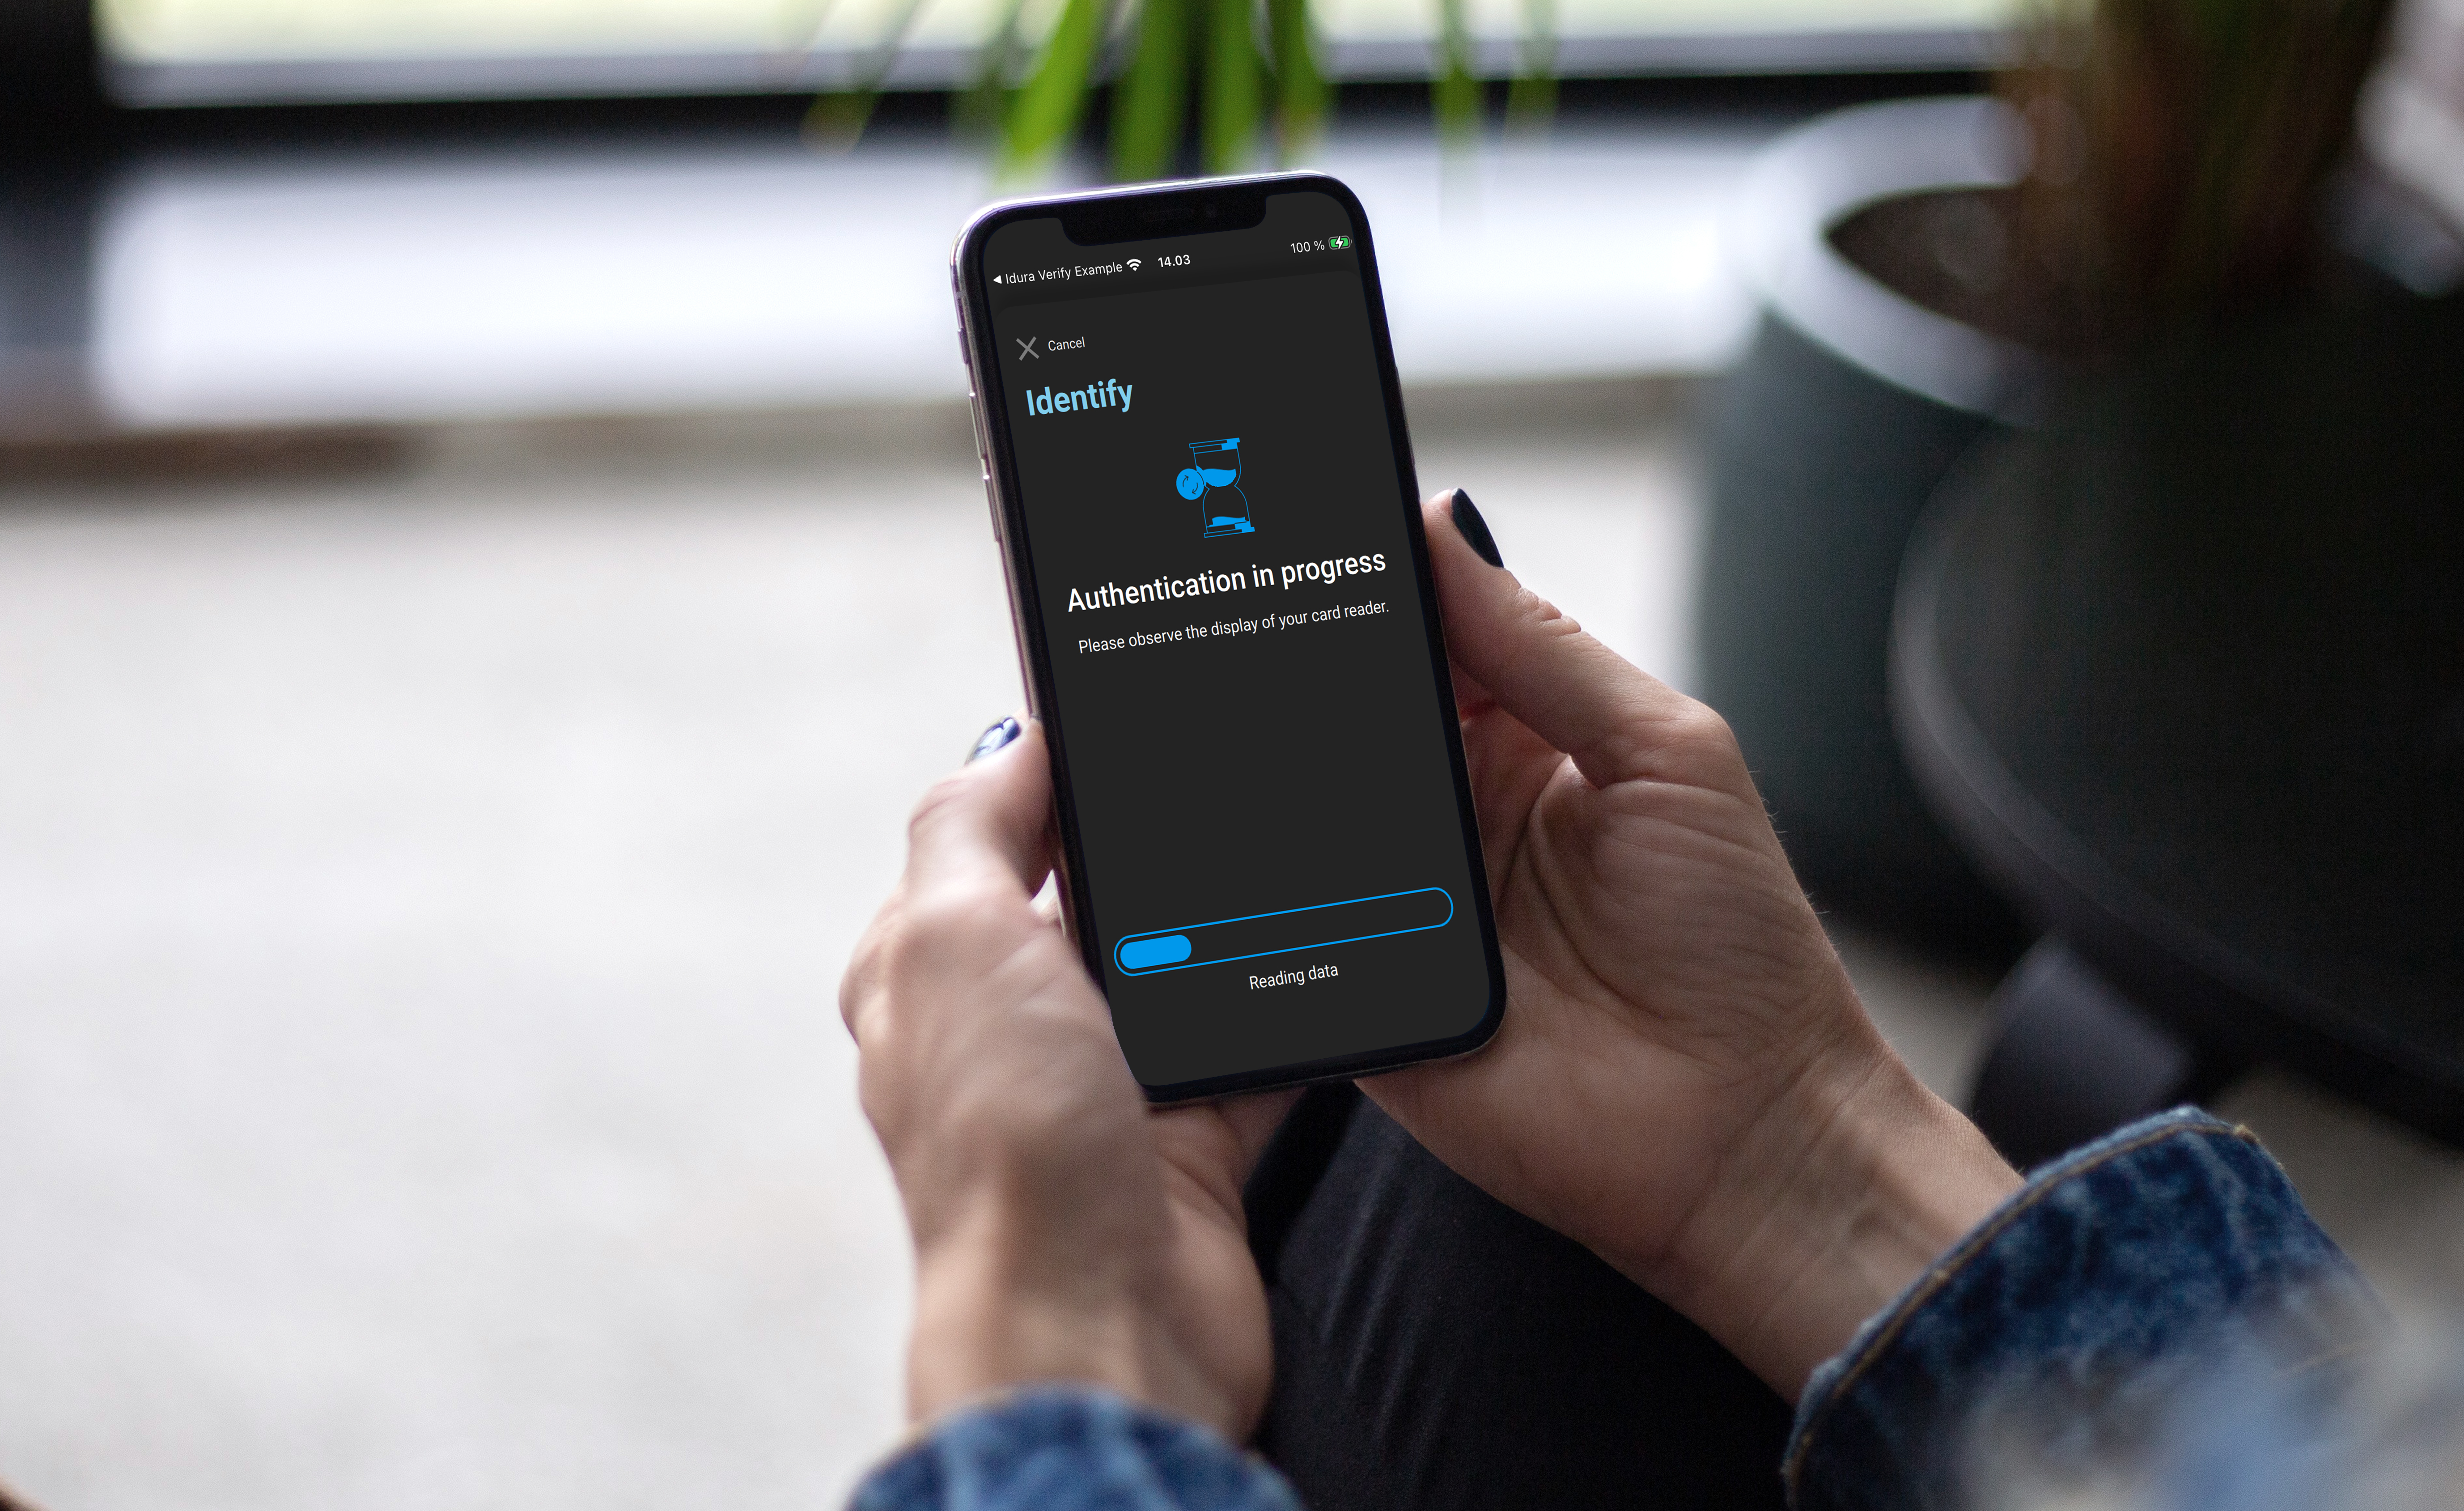
The organization specifically highlights OpenID Connect Client-Initiated Back-Channel Authentication (CIBA). The standard enables, say, a bank or public authority to send an authentication request to a caller's digital identity app during a call. The caller can then prove who they are without disclosing personal information.
“We have long known that knowledge-based authentication is not secure. This breach is a reminder to anyone still relying on it that they are exposing themselves and their customers to serious risk. Fortunately, better solutions are available, and choosing technology based on OpenID standards makes it straightforward to integrate with a wide range of vendors,” says Frederik Krogsdal Jacobsen, co-chair of the OpenID Foundation’s AB/Connect Working Group and lead software engineer at the Danish identity company Idura.
Open standards make it easier to switch providers
According to the OpenID Foundation, a key advantage of using international, open standards is that companies are not locked into a single technology provider. At the same time, solutions can be verified against common security requirements.
However, the organization emphasizes that phone-based authentication must be linked securely to the specific call to prevent phishing and manipulation.
“CIBA was precisely created to take care of such cases. Using it, organizations can improve their security posture and protect their customers better,” says Bjorn Hjelm, co-chair of the OpenID Foundation’s MODRNA Working Group, which developed CIBA.
Read the OpenID Foundation’s blog post: "Lessons from Denmark’s CPR breach"
About the OpenID Foundation
The OpenID Foundation is an international nonprofit organization that's been developing open standards for secure digital identity and authentication since 2007. Its OpenID Connect standard is used by millions of applications worldwide. Learn more at openid.net.